 Technology22 Sept 2026
Stolen Passwords Leave U.S. Water Providers Vulnerable to Hackers
Research reveals that over 1,700 U.S. water providers are vulnerable to hackers due to stolen passwords, highlighting cybersecurity risks.
Introduction
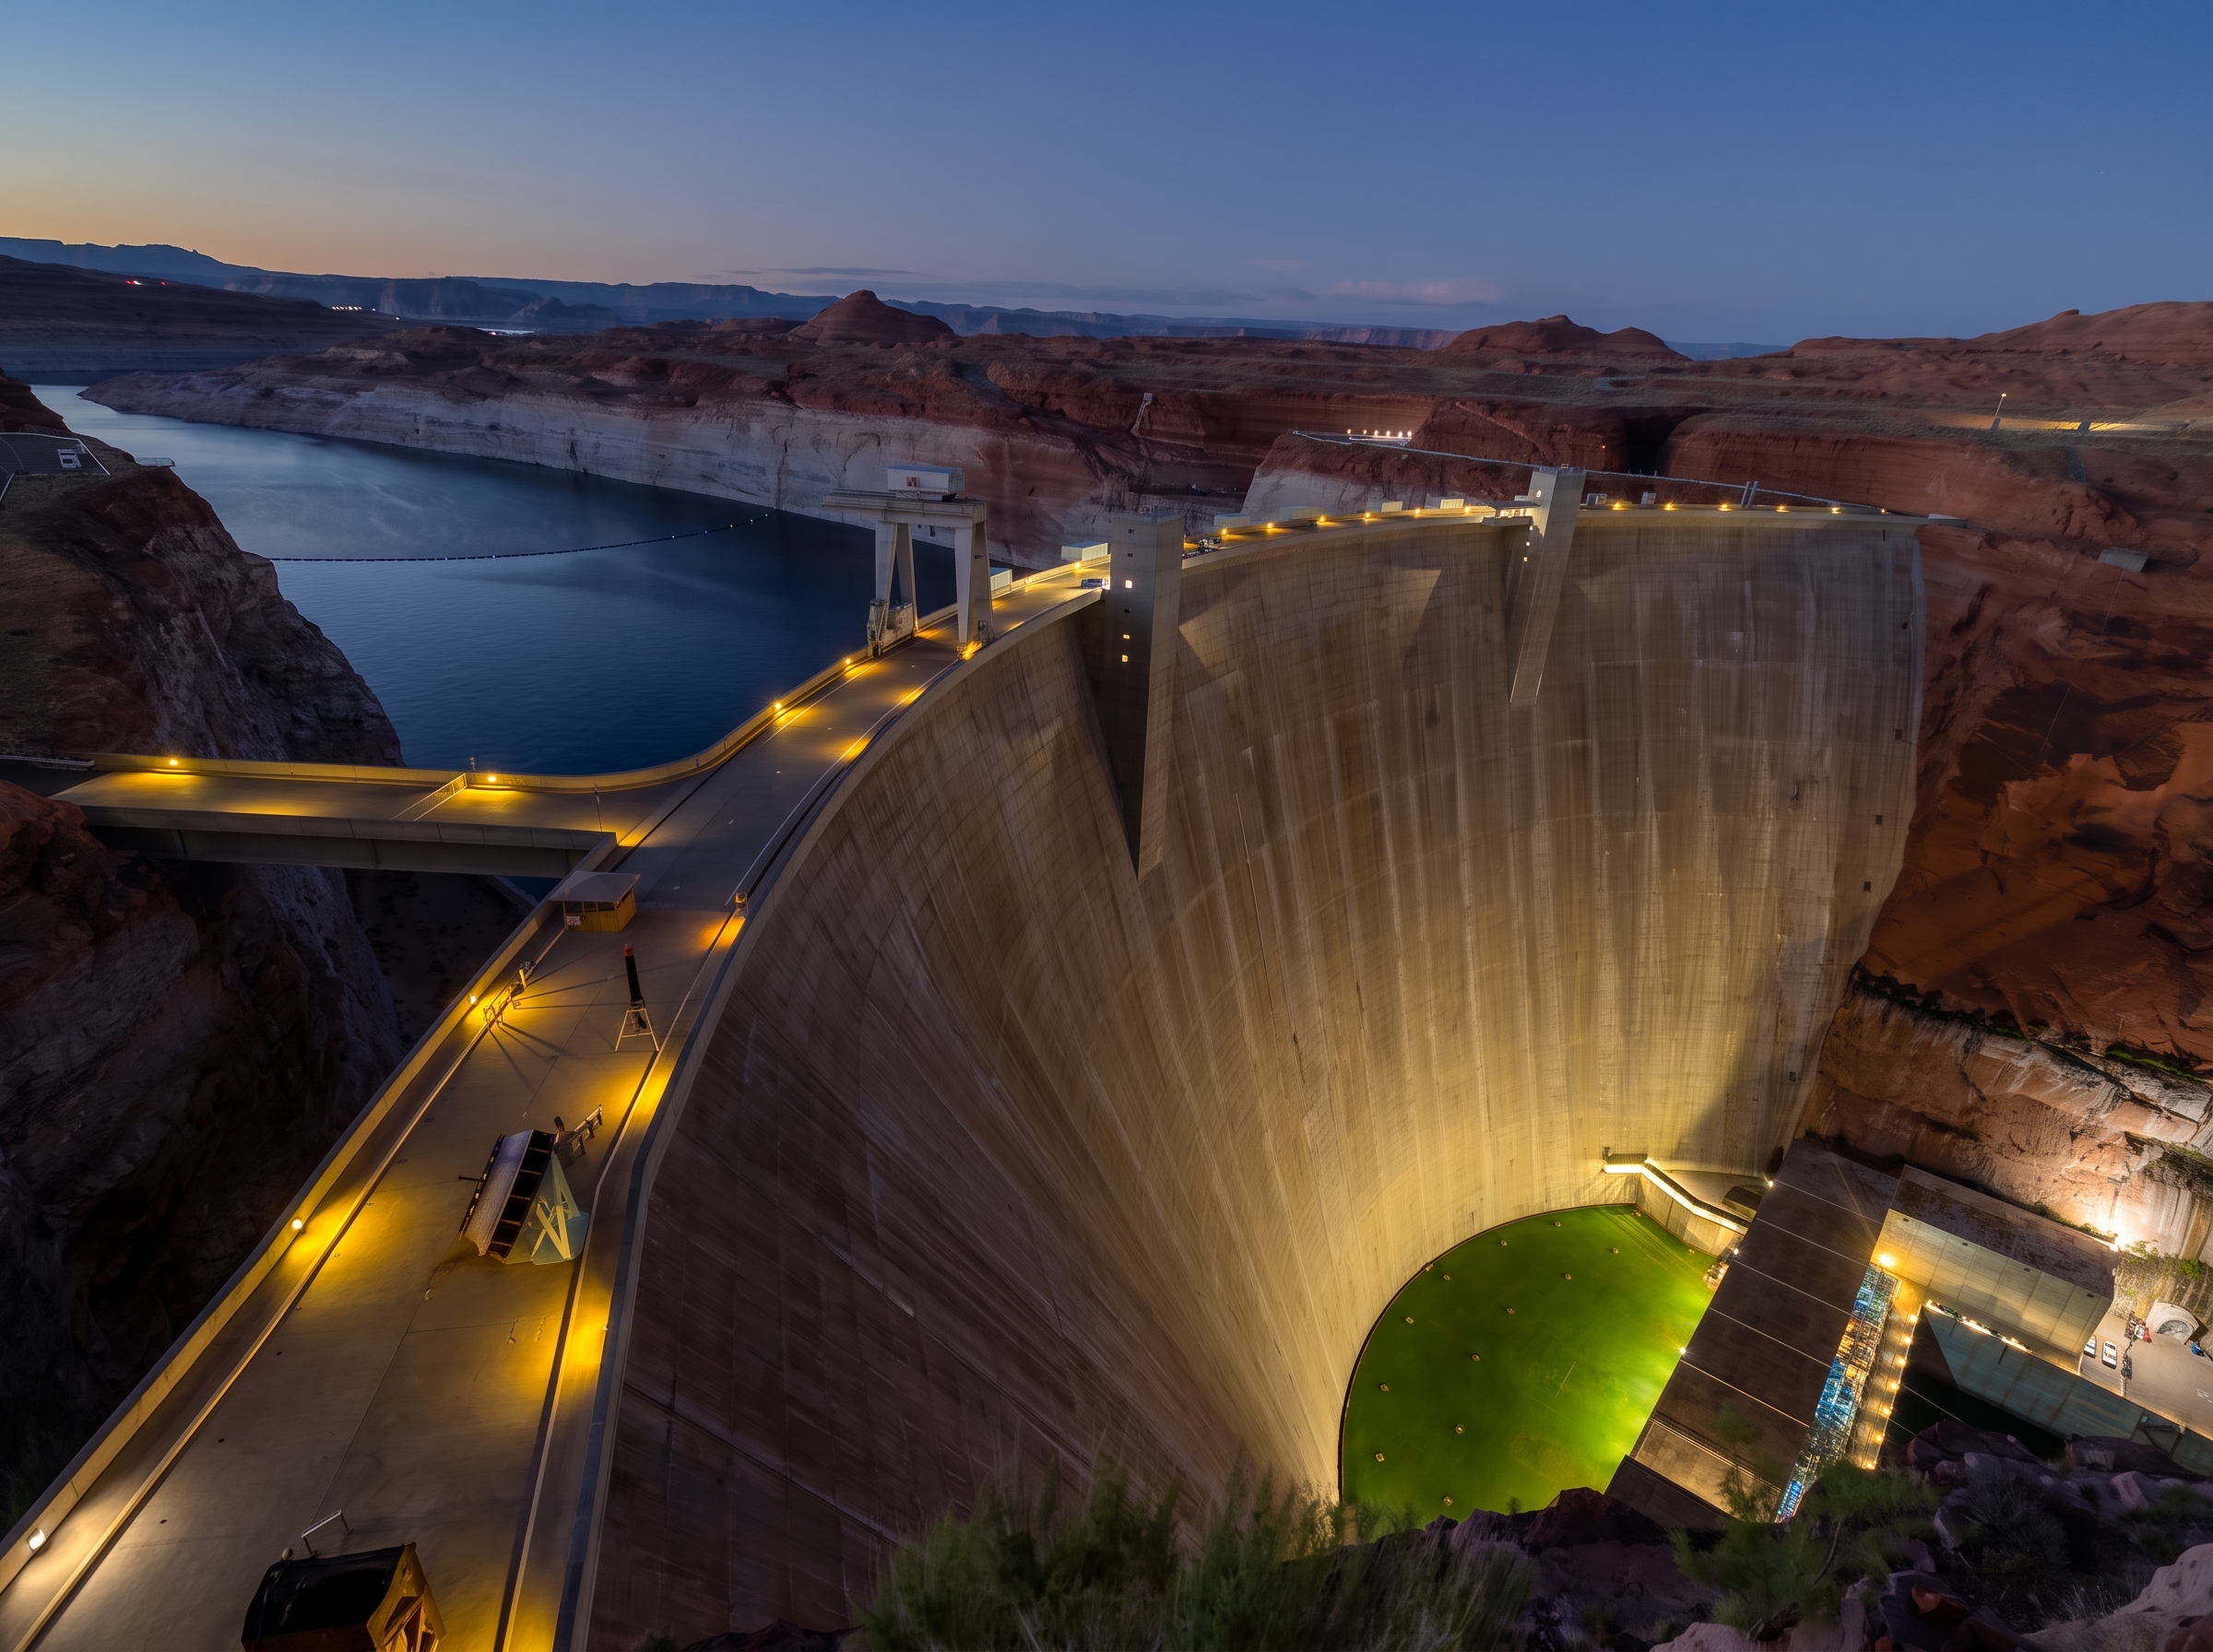
Recent research by SpyCloud has unveiled alarming vulnerabilities in the cybersecurity of over 1,700 U.S. water and wastewater providers. The study emphasizes how easily hackers can breach critical infrastructure using malware designed to steal employee passwords, raising significant concerns about national safety and water supply security.
Findings on Malware and Security Risks
The analysis conducted by SpyCloud focuses on password-stealing malware, which has emerged as a potent threat to water providers across the U.S. Unlike sophisticated attack methods requiring advanced AI tools, this malware offers hackers a straightforward way to gain unauthorized access to sensitive operational networks.
Vulnerability Metrics
According to SpyCloud, which maintains a comprehensive database of over 66,000 public-facing systems registered with the U.S. Environmental Protection Agency (EPA), approximately 1,787 organizations—nearly 20% of those analyzed—were found to have had their passwords compromised. Alarmingly, at least 250 organizations had credentials that could directly access their operational networks and remote access systems, critical for managing water supply and infrastructure effectively.
A particular incident highlighted by SpyCloud involved a metering technology provider, which unknowingly hosted a device infected with password-stealing malware. This breach allowed attackers to acquire passwords used by 167 different U.S. utility companies connected to the provider, demonstrating the ripple effect of such security weaknesses.
The Nature of Password-Stealing Malware
Password-stealing malware, referred to as infostealers, functions by extracting stored passwords and session tokens. These tokens grant hackers access that can bypass even multi-factor authentication, posing severe risks. Criminal networks often trade these stolen credentials to facilitate further breaches, particularly targeting organizations with critical infrastructure.
Recent Cybersecurity Challenges
These findings come on the heels of a surge in cyberattacks against water providers nationwide, reportedly linked to Iran-backed hackers. However, SpyCloud’s research did not find that these attacks specifically utilized stolen passwords. Instead, they pointed to vulnerabilities created by unaddressed security flaws, such as default passwords on mechanical equipment and controllers that are integral to water infrastructure management.
SpyCloud emphasized that the issue of stolen passwords serves as a continual threat for organizations that might be unaware or unprepared for such intrusions. Jason Lancaster, Chief Investigations Officer at SpyCloud, highlighted the dual narrative that the water sector must navigate; not only traditional malware threats but also the pervasive risk posed by shared security weaknesses across technology utilized in critical infrastructure.
Conclusion
The growing trend of password theft poses a significant risk to America's water sector, prompting calls for enhanced cybersecurity measures. As various entities work to strengthen their defenses, the emphasis must remain on safeguarding sensitive operations integral to public health and safety.
For the future, experts assert that it is essential for water providers to mitigate these risks and strengthen their cybersecurity protocols to prevent falling victim to such breaches.
Popular news
António Guterres urges a global ban on autonomous weapons, emphasizing the ethical risks of AI in military decisions.
Subscribe to
our news
Get the most important updates and top stories in your inbox.